
Architecting Enterprise Defense with Unshakeable Confidence
Lumiverse Solutions delivers end-to-end offensive cyber security, statutory compliance audits (RBI, SEBI, IRDAI, UIDAI, ISO 27001, SOC 2, HIPAA), 24/7 Managed SOC operations, incident response forensics, and AI-powered security products.
- ISO 27001 / PIMS Compliant ✓
- SOC 2 Type II Compliant ✓
- RBI / SEBI CSCRF Compliant ✓
- UIDAI & DPDP Compliant ✓
Our Clients
Lumiverse Solutions helps organizations identify risks, strengthen defenses, and stay compliant in an evolving threat landscape.
Our Services
Lumiverse Solutions helps organizations identify risks, strengthen defenses, and stay compliant in an evolving threat landscape.
Securing Every Industry, Every Day
Industry-focused security testing to protect what matters most to your business. Explore All Verticals →
Strengthen Trust. Secure Every Transaction.
We help BFSI organizations protect sensitive data, ensure compliance, and stay ahead of evolving cyber threats.
Data Breaches & Financial Fraud
Protect sensitive customer and financial data from breaches and fraudulent activities.
Regulatory Compliance
Meet RBI, ISO 27001, PCI-DSS and other regulatory requirements with confidence.
Third-Party & API Risks
Secure third-party integrations, APIs, and digital channels from vulnerabilities.
Protecting Health. Securing Trust.
We help healthcare organizations secure patient data, ensure compliance, and deliver safe, uninterrupted care.
Sensitive Patient Data Protection
Safeguard personal health information (PHI) from breaches and unauthorized access.
Regulatory Compliance
Stay compliant with HIPAA, HITECH, and other healthcare security standards.
Connected Medical Devices Security
Secure IoT-enabled medical devices and prevent risks in connected environments.
Secure Operations. Strengthen Resilience.
We help manufacturing organizations protect critical systems, intellectual property, and supply chains from cyber threats.
OT & ICS Security
Protect industrial control systems and critical infrastructure from cyberattacks and disruptions.
Supply Chain & Third-Party Risks
Identify vulnerabilities across your supply chain and trusted vendor ecosystem.
Intellectual Property Protection
Safeguard designs, formulas, and sensitive IP from theft and unauthorized access.
Secure Transactions. Build Customer Trust.
We help retail businesses protect customer data, secure transactions, and prevent fraud across all channels.
Protect Customer & Payment Data
Secure sensitive customer information and card details from breaches and misuse.
Prevent Fraud & Account Takeover
Detect and prevent fraudulent activities and unauthorized account access.
Ensure Compliance & Data Privacy
Stay compliant with PCI DSS, GDPR, and other data protection regulations.
Innovate Securely. Protect What Powers the Future.
We help technology companies build secure products, protect digital assets, and manage evolving cyber risks across the software lifecycle.
Secure Applications & APIs
Identify and fix vulnerabilities in web, mobile, and API applications before attackers exploit them.
Cloud & Infrastructure Security
Strengthen cloud configurations and secure your infrastructure across multi-cloud environments.
DevSecOps & Continuous Security
Embed security early in the SDLC with automated testing and continuous monitoring.
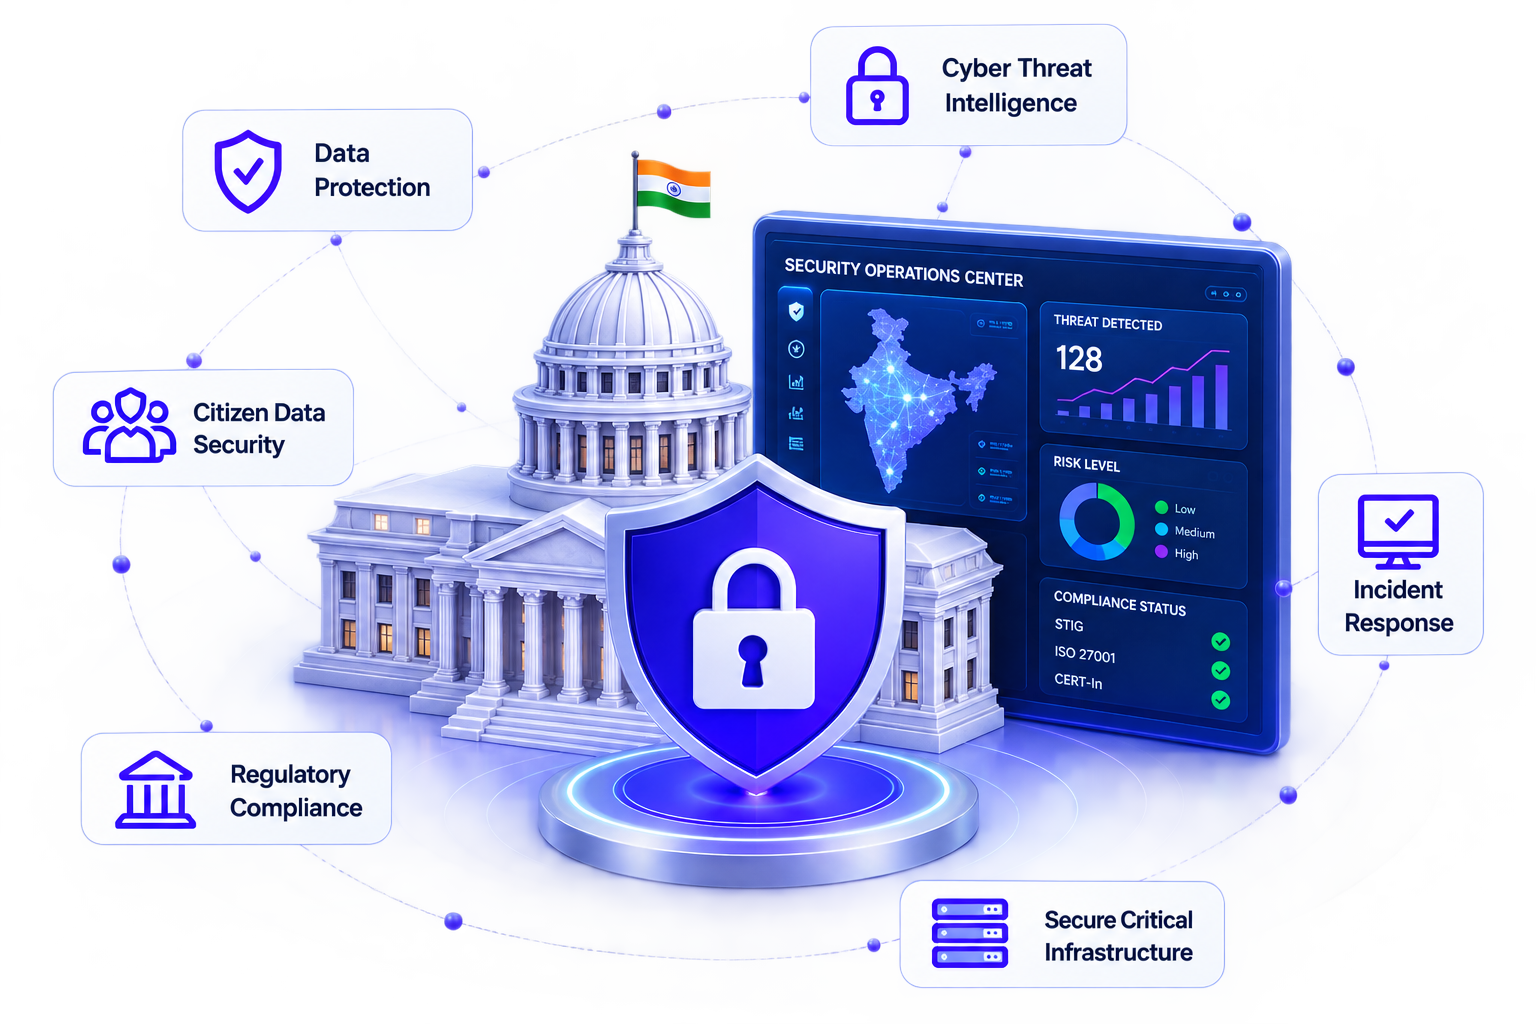
Protect Citizens. Secure Nations.
We help government agencies secure critical infrastructure, protect sensitive data, and ensure continuity of essential services.
Protect Sensitive Data & Citizen Information
Safeguard confidential government data and citizen information from breaches and unauthorized access.
Ensure Compliance & Policy Adherence
Meet regulatory requirements including CERT-In guidelines, ISO 27001, STIG, and other government standards.
Secure Critical Infrastructure & Services
Strengthen resilience of critical systems and ensure uninterrupted delivery of essential services.
Everything Your Business Needs To Stay Resilient
Explore our six core cybersecurity service practices engineered for modern cloud, financial, and digital enterprises.
Cybersecurity Assessment (VAPT)
- Web Application VAPT
- Mobile App VAPT (iOS/Android)
- Multi-Cloud Security (AWS/Azure)
- API & Microservices Security
Incident Response & Forensics
- Rapid Breach Containment
- Digital Forensics & Chain of Custody
- Malware Reverse Engineering
- CERT-In 6-Hour Reporting SLAs
Compliance, Standards & Regulatory Audits
- ISO 27001:2022 & ISO 27701
- SOC 2 Type I & Type II Audits
- RBI CSF & SAR Audits
- SEBI CSCRF Capital Market Audits
Managed Cyber SOC & SIEM
- 24×7 Active Threat Hunting
- SIEM & SOAR Telemetry Integration
- Dark Web Threat Intelligence Ingestion
- Endpoint Detection & Response (EDR)
Specialized Red Teaming
- Social Engineering & Phishing
- IoT & Embedded Firmware VAPT
- Smart Contract & Web3 Audits
- SAST Secure Code Review
Audited Against World-Class Regulatory Frameworks
Our certified security practitioners hold CISA, CISSP, CEH, OSCP, and DISA credentials ensuring 100% regulatory acceptance.
 OSCP - Offensive Security Certified Professional
 CEH - Certified Ethical Hacker
 CISSP - Certified Information Systems Security Professional
 CISA - Certified Information Systems Auditor
 CISM - Certified Information Security Manager
 AWS Certified Security
 Microsoft Azure Security Certified
 ISO 27001 Lead Auditor
 ISO 27001 Lead Implementer
 PCI Professional QSA
 ISO 22301 Lead Implementer
 CRISC - Certified in Risk & Information Systems
 CHFI - Computer Hacking Forensic Investigator
 Red Hat Certified Specialist
 eJPT - Junior Penetration Tester
 CCNA - Cisco Certified Network Associate
 CDPSE - Certified Data Privacy Solutions Engineer
 OSCE - Offensive Security Certified Expert
 LPT - Licensed Penetration Tester
OSCP - Offensive Security Certified Professional
CEH - Certified Ethical Hacker
CISSP - Certified Information Systems Security Professional
CISA - Certified Information Systems Auditor
CISM - Certified Information Security Manager
AWS Certified Security
Microsoft Azure Security Certified
ISO 27001 Lead Auditor
ISO 27001 Lead Implementer
PCI Professional QSA
ISO 22301 Lead Implementer
CRISC - Certified in Risk & Information Systems
CHFI - Computer Hacking Forensic Investigator
Red Hat Certified Specialist
eJPT - Junior Penetration Tester
CCNA - Cisco Certified Network Associate
CDPSE - Certified Data Privacy Solutions Engineer
OSCE - Offensive Security Certified Expert
LPT - Licensed Penetration Tester
Why Leading CISOs Choose Lumiverse Solutions
We combine elite offensive ethical hacking with rigorous compliance precision to safeguard your revenue and brand reputation.
100% Manual Deep Exploitation
Automated tools miss business logic flaws, multi-tenant leaks, and token replay bugs. Our certified offensive researchers manually test every API parameter and user flow.
Zero False Positives Guarantee
Every vulnerability is manually validated with proof-of-concept (PoC) screenshots, step-by-step reproduction steps, and exact developer remediation code snippets.
Complimentary Retesting Windows
Every VAPT and statutory audit includes a 30-day free retesting period to ensure internal engineering fixes have completely closed all identified risk vectors.
Rapid 4-Hour Response SLA
From initial scoping to emergency incident containment, our senior security architects deliver actionable scoping proposals and technical debriefs within 4 hours.
5-Stage Enterprise Cyber Defense Roadmap
A transparent, predictable methodology designed for minimal engineering disruption and rapid regulatory sign-off.
Architecture Intake & Threat Modeling
Defining target boundaries, cloud subscriptions, API endpoints, white/grey-box methodology, and establishing safe testing Rules of Engagement (RoE).
Deep Penetration Testing & Gap Assessment
Certified ethical hackers execute manual exploit chaining, API authorization bypasses, and evaluate governance policies against applicable statutory standards.
Prioritized Remediation & Developer Walkthrough
Delivering prioritized CVSS v3.1 vulnerability matrices with step-by-step reproduction steps, PoC screenshots, and holding live engineering walkthrough sessions.
Patch Verification & 100% Control Closure
Re-assessing patched software builds and revised cloud configurations to guarantee that vulnerabilities are securely and permanently remediated.
Official CERT-In Safe-to-Host & Board Reports
Delivering the final Executive Summary, Board IT Committee compliance filing packages, and the official Lumiverse Safe-to-Host Security Certificate.
What Enterprise Leaders Say About Us
Hear directly from CISOs, CTOs, and Compliance Directors who trust Lumiverse Solutions for their mission-critical security.
"Lumiverse Solutions guided us through a complex RBI Cyber Security Framework audit seamlessly. Their manual VAPT identified critical business logic vulnerabilities that automated tools missed, and their team supported our developers until 100% closure."
"Achieving SOC 2 Type II compliance was essential for our US enterprise expansion. Lumiverse's automated evidence workflows and readiness team made the entire process painless. We passed our CPA attestation with zero non-conformities."
"Their SEBI Cyber Resilience audit package and Action Taken Report (ATR) filing enabled us to clear exchange compliance well ahead of schedule. Truly the most professional and technically proficient cybersecurity partner in India."
Everything You Need to Know About Our Services
Clear answers on scoping, test safety, regulatory compliance, and timelines.